Product identity
Manufacturer SKU, MPN, and model information
Use the manufacturer’s SKU, MPN, model identifier, or configuration code to match the exact equipment and variant.
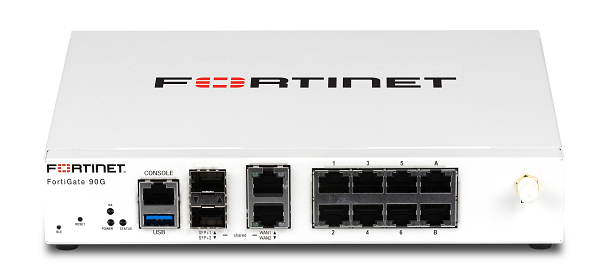
Fortinet FortiGate 90G
- Manufacturer identifier
- FG-90G
- Variant
- FortiGate 90G base appliance model
- Region
- Global
- Verified
- Official source
- Manufacturer verification
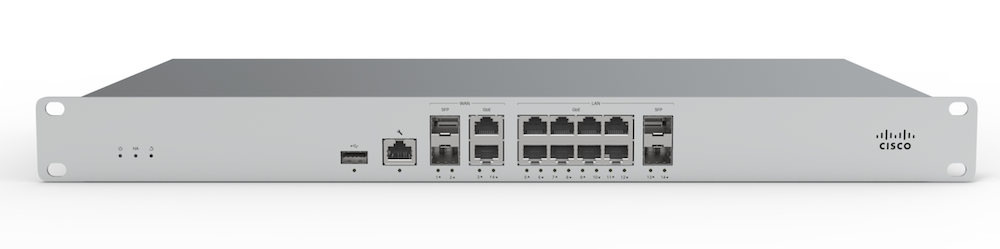
Cisco Meraki MX85
- Manufacturer identifier
- MX85-HW
- Variant
- Cisco Meraki MX85 hardware appliance
- Region
- Global
- Verified
- Official source
- Manufacturer verification
Sophos XGS 128 Gen 2
- Manufacturer identifier
- XGS 128
- Variant
- Gen.2 wired appliance model identifier
- Region
- Global
- Verified
- Official source
- Manufacturer verification
A branch firewall is purchased for protected service
The useful question is how the branch performs with its intended controls enabled. A basic forwarding result excludes much of the work that motivates buying a next-generation firewall in the first place.
Inventory the applications and traffic that matter: encrypted business services, voice, local-to-cloud transfers, remote users and any site-to-site paths. Identify the concurrency and peak periods, not just an average internet-utilization number.
Then define the policy that must remain active. A performance demonstration that turns off the required inspection is testing a different product configuration from the one the business intends to operate.
Keep different throughput measurements separate
Vendors publish firewall, application-control, threat-protection and encrypted-inspection figures under different conditions. These numbers can help identify a plausible capacity class, but they should not be combined into a single synthetic score.
The FortiGate 90G and Sophos XGS 128 Gen 2 illustrate the issue: each has several published performance measures that answer different questions. Their physical interface rates also do not establish inspected throughput.
Shortlist with enough capacity for the intended service, then test representative traffic with the production policy. A modest branch may not require a maximum-load laboratory exercise, but it does need evidence that the important applications remain usable.
Choose a direction from the operating requirement
The table is a starting point. It does not make these appliances equal in every capacity dimension or suggest that one ecosystem is best for every branch.
Select the actual model and options. Shared-media interfaces are alternatives, storage-equipped variants change local-logging choices, and nearby model numbers can use different processor architectures.
| Requirement | Candidate direction | Reason to choose it |
|---|---|---|
| Fortinet operating environment and 10G links | FortiGate 90G | Interface and platform fit, with current remote-access behavior checked |
| Sophos environment and several multigigabit copper links | XGS 128 Gen 2 | Branch layout and management fit |
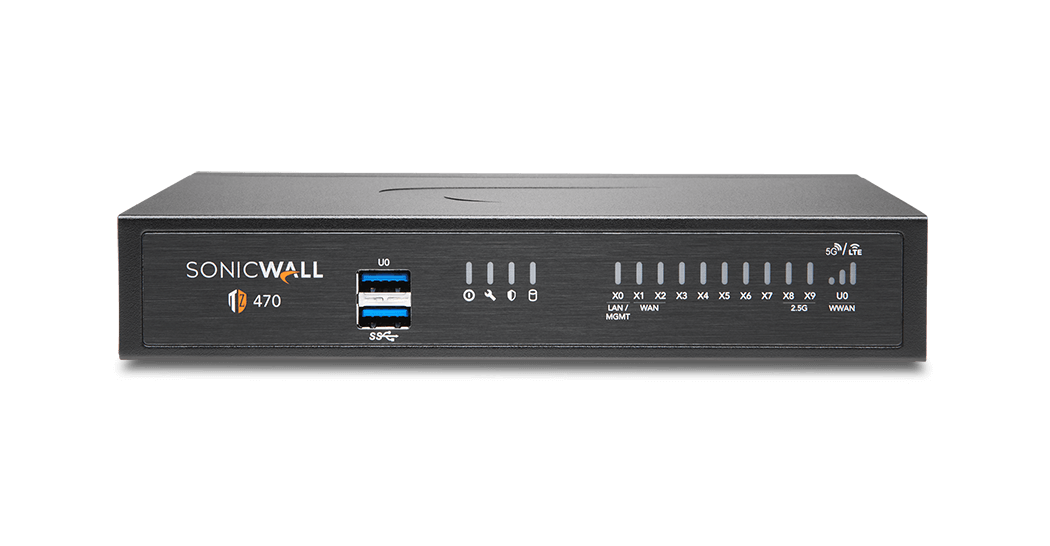
| Existing SonicWall TZ470 installation | Lifecycle-led retain or migrate decision | Remaining service requirements differ from new-platform selection |
| Existing Meraki operation | MX85 as a platform-fit comparison | Use the approved product review and a current workload-sized configuration |
Software changes can create a migration project
Remote-access VPN is a particularly important example. Newer FortiOS release paths changed SSL-VPN tunnel availability, so an old performance figure is not a durable promise of that workflow in every current version.
Before ordering, establish the supported client, authentication and access-policy arrangement. A hardware replacement that also changes how employees connect should include that migration explicitly.
Operator reports of stability on older firmware are useful historical evidence, not a reason to install an outdated release. The selected version should be supported for the exact model and validated against the organization's applications.
Lifecycle and service terms change the value of a low price
SonicWall's TZ470 reached last-time-buy in June 2026. That event is not the same as the end of all support, but it changes the rationale for a fresh purchase. Maintaining an installed fleet and selecting a new standard are different decisions.
Compare the required operating period with the current support and subscription arrangement. Include the services needed for inspection, updates, management and logging rather than comparing bare appliances alone.
A discounted unit can remain sensible for a specific continuity requirement. It can also become poor value when its remaining lifecycle or migration burden fails to match the intended deployment. The quote should make that tradeoff visible.
Acceptance should exercise applications and recovery
A reported XGS 128 cloud-voice problem illustrates why an internet speed test is insufficient. The discussion did not establish a model-wide defect, but it exposed a real application path that needed investigation.
Exercise call setup and media, remote authentication, reconnects and the important business transactions through the intended policy. For a redundant design, repeat the relevant work through the failure transition the business expects to survive.
Finally, confirm that the team can recover access, identify the running configuration and escalate an incident. A firewall purchase is successful when the protected branch keeps working and can be restored predictably, not merely when the appliance reaches its advertised throughput.
Onsite installation support
Need help deploying the technology you select?
Cartennas provides onsite installation, replacement, rack mounting, cabling, and Smart Hands support for business security and firewall equipment across the United States.
Request Installation SupportCartennas assessment
Select a firewall around the complete protected workload and operating period. Verify software-dependent remote access, price the required subscriptions and logging, and make application behavior and recovery the final acceptance criteria.
Cartennas buying analysis grounded in exact product configurations, manufacturer documentation and available firsthand operating evidence. Review methodology. Cartennas provides product procurement and onsite services. Product review terms.
Official manufacturer information
Confirm the exact model, specifications, licensing, warranty, and support terms directly with the manufacturer.
- Fortinet: Fortinet product matrix
- Fortinet: NGFW ordering guide
- Fortinet: SSL-VPN to IPsec migration introduction
- Sophos: Second-generation XGS desktop specifications and methodology
- SonicWall: TZ270 and TZ470 last-time-buy announcement
- SonicWall: Gen 7 TZ Series data sheet
Product information was checked on September 5, 2026. Specifications, licensing, warranty, availability, and pricing can change.